Cybersecurity Careers: Red Team vs. Blue Team Differences
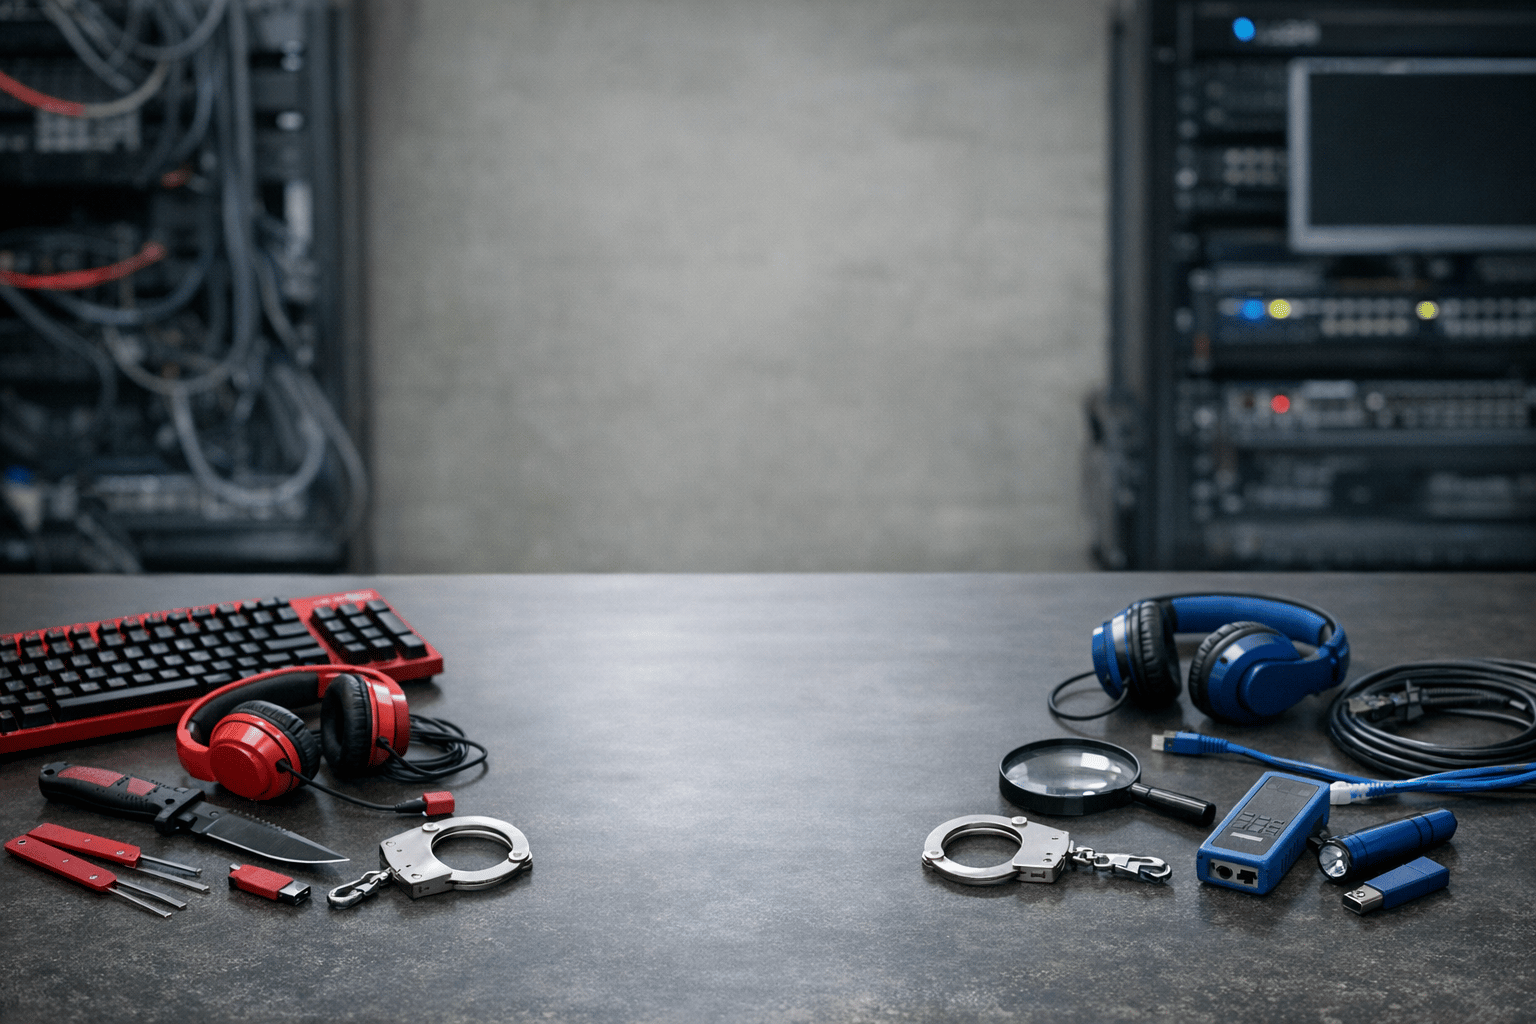
Red Team and Blue Team differ fundamentally in their offensive and defensive roles. The Red Team acts as the "attackers," simulating cyberattacks and identifying security vulnerabilities. In contrast, the Blue Team serves as the "defenders," continuously monitoring, detecting threats, and responding to incidents to protect organizational assets. While both teams share the ultimate goal of strengthening overall system security, their day-to-day methods, mindsets, and skill sets operate on completely different fronts.
What is the Red Team, and How Do They Work?
The Red Team is a group of cybersecurity professionals who emulate real-world malicious adversaries and hackers (Adversary Emulation). Their mission is to evaluate whether an organization's security posture can withstand genuine attacks. This team employs various tactics and techniques used by real threat actors to uncover weaknesses before attackers can exploit them.
Key roles and responsibilities of the Red Team include:
- Vulnerability Assessment & Penetration Testing: Auditing networks, websites, servers, and applications to uncover security gaps and attempting to exploit them.
- Social Engineering: Testing human vulnerabilities by conducting simulated phishing campaigns or phone-based pretexts to evaluate employee security awareness.
- Red Teaming Exercises: Executing full-scale, unannounced simulated intrusions to assess how effectively and rapidly the Blue Team and automated defenses detect and neutralize threats.
- Vulnerability Reporting: Documenting the exploitation path and providing technical remediation recommendations to developers and management.
Common tools utilized by the Red Team include Kali Linux, Metasploit, Burp Suite, Nmap, and Cobalt Strike.
---
What is the Blue Team, and How Do They Work?
The Blue Team represents the internal defenders responsible for continuously maintaining the security of an enterprise's infrastructure, data, and networks. Rather than attempting to break into systems, their primary focus is building resilient defenses, monitoring for anomalies, and mitigating active attacks in real time.
Key roles and responsibilities of the Blue Team include:
- Monitoring & Detection: Operating inside a Security Operations Center (SOC) to monitor enterprise environments 24/7 by analyzing system, application, and security event logs.
- Incident Response: Taking immediate action when a breach or compromise occurs, such as isolating infected hosts from the network and restoring critical services.
- Digital Forensics: Performing post-incident investigations to determine the root cause of an attack, trace the adversary's lateral movements, and assess total damage.
- Hardening & Patching: Proactively securing network devices, configuring firewalls, managing Intrusion Detection/Prevention Systems (IDS/IPS), and routinely patching vulnerabilities.
Common tools utilized by the Blue Team include Splunk, Wireshark, CrowdStrike, Suricata, and various SIEM (Security Information and Event Management) platforms.
---
Red Team vs. Blue Team: Practical Differences
To clearly understand the operational differences between both sides, their core responsibilities, mindsets, and required skill sets are compared below:
| Comparison Area | Red Team (Offensive) | Blue Team (Defensive) |
|---|---|---|
| Primary Objective | Identify flaws and exploit vulnerabilities | Protect systems, detect intrusions, and mitigate attacks |
| Mindset | Attacker perspective (thinks creatively to find an entry point) | Analytical and defensive perspective (thorough, rigorous, verifies every vector) |
| Work Style | Project-based or engagement-driven operations | Continuous 24/7 operations (often shift-based) |
| Core Skills | Scripting, Reverse Engineering, Exploit Development | Log Analysis, Network Traffic Inspection, System & Network Administration |
| Example Tools | Metasploit, Burp Suite, Kali Linux | Splunk, Wireshark, SIEM, EDR |
| Job Roles | Penetration Tester, Ethical Hacker, Vulnerability Assessor | SOC Analyst, Incident Responder, Forensics Investigator |
---
Cybersecurity Beginners: Which Team Should You Choose?
Choosing between Red Team and Blue Team largely depends on your personal interests, technical background, and working style:
- Choose Red Team if: You enjoy solving intricate puzzles, breaking into systems to uncover flaws, experimenting with new exploit techniques, and coding or scripting custom tools. However, offensive roles usually demand a solid foundational understanding of system and network architecture, which often requires significant hands-on lab practice beforehand.
- Choose Blue Team if: You enjoy investigative analysis, root-cause troubleshooting, and understanding how corporate networks operate end-to-end. The Blue Team track—particularly entry-level SOC Analyst (Tier 1) roles—offers more job openings for newcomers, as virtually every organization with IT infrastructure requires round-the-clock internal monitoring.
Beyond these two disciplines, the industry also embraces the Purple Team concept. Rather than being a separate, standalone team, Purple Teaming is a collaborative methodology where the Red Team shares its attack techniques and the Blue Team immediately incorporates those insights into its detection engineering, maximizing security posture across the organization.
---
Frequently Asked Questions
Do you have to stay committed to only one side throughout your career?
Not at all. The skills from both disciplines complement each other significantly. Professionals with prior Blue Team experience possess deep knowledge of system architectures and security controls, making them adept at evading detection when transitioning to the Red Team. Conversely, former Red Teamers understand adversary tactics firsthand, allowing them to engineer far more effective defensive controls within a Blue Team.
Which team has more job openings in the market?
Blue Team roles have noticeably higher market demand. Every mid-to-large enterprise running internal IT infrastructure needs dedicated staff for ongoing monitoring and defensive operations. In contrast, dedicated Red Team positions are more commonly concentrated within specialized cybersecurity consultancies, MSSPs, or contract-based penetration testing engagements, resulting in fewer overall openings.
Can you land a Blue Team role without a programming background?
Yes, you can get started without deep programming skills. An entry-level foundation focused on computer networking, Windows/Linux operating system internals, and basic log analysis is sufficient to begin as a Tier 1 SOC Analyst. That said, picking up scripting languages like Python or PowerShell later on will significantly enhance your automation capabilities and open up senior analytical roles.
Which certifications are best for starting out in each path?
For general beginners, CompTIA Security+ serves as an excellent vendor-neutral foundation covering core concepts for both sides. Those looking to pursue the Red Team path should focus on hands-on practical certifications such as eJPT (eLearnSecurity Junior Penetration Tester) or OSCP. For those targeting the Blue Team path, specialized credentials like CompTIA CySA+ or BTL1 (Blue Team Level 1) are highly regarded for validating incident detection and threat response capabilities.
Tags
AlphaSpace Course
AlphaSpace Course
Please log in to comment
No comments yet
Be the first to comment!
Want to learn more?
Explore our online courses and valuable membership packages